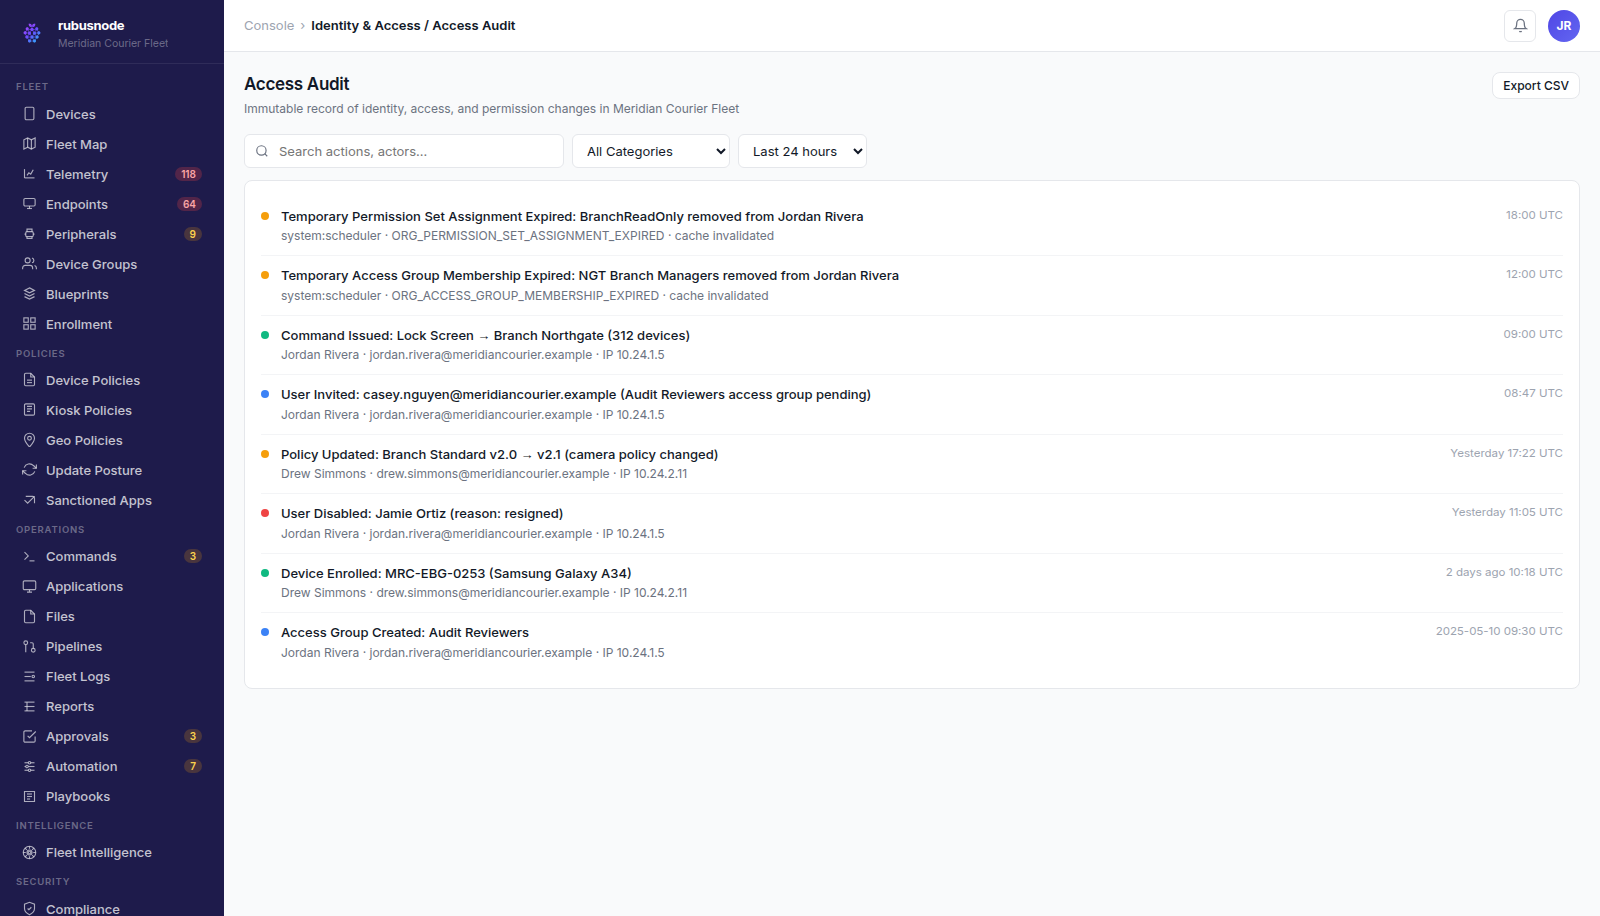
Access audit trail in the RubusNode console.
Approval-gated operations for sensitive actions
PBAC and MFA scope who can act on which devices, and sensitive operations — wipes, policy exceptions, restricted state changes — route through an approval workflow before they execute.
- PBAC and MFA on every action
- Approval workflows for high-risk operator actions
- Role-scoped access for branch, security, and compliance teams
Audit evidence built for regulators
Every identity, access, and permission change is recorded in a hash-chained, immutable audit trail, with compliance evidence exports for regulated reviews rather than a manual reconstruction after the fact.
Geo-fencing and branch-bound compliance
Geo-fencing policy ties device compliance to physical branch or facility location, and OS-update posture keeps regulated device fleets on a governed patch cadence.
Common questions
Does approval-gating slow down routine fleet operations?
Approval gates apply to sensitive, high-risk actions — wipes, policy exceptions, restricted state changes — not routine operations, so day-to-day fleet management stays fast.
See how RubusNode fits your endpoint fleet.
Book a walkthrough for this capability and the rest of the platform.