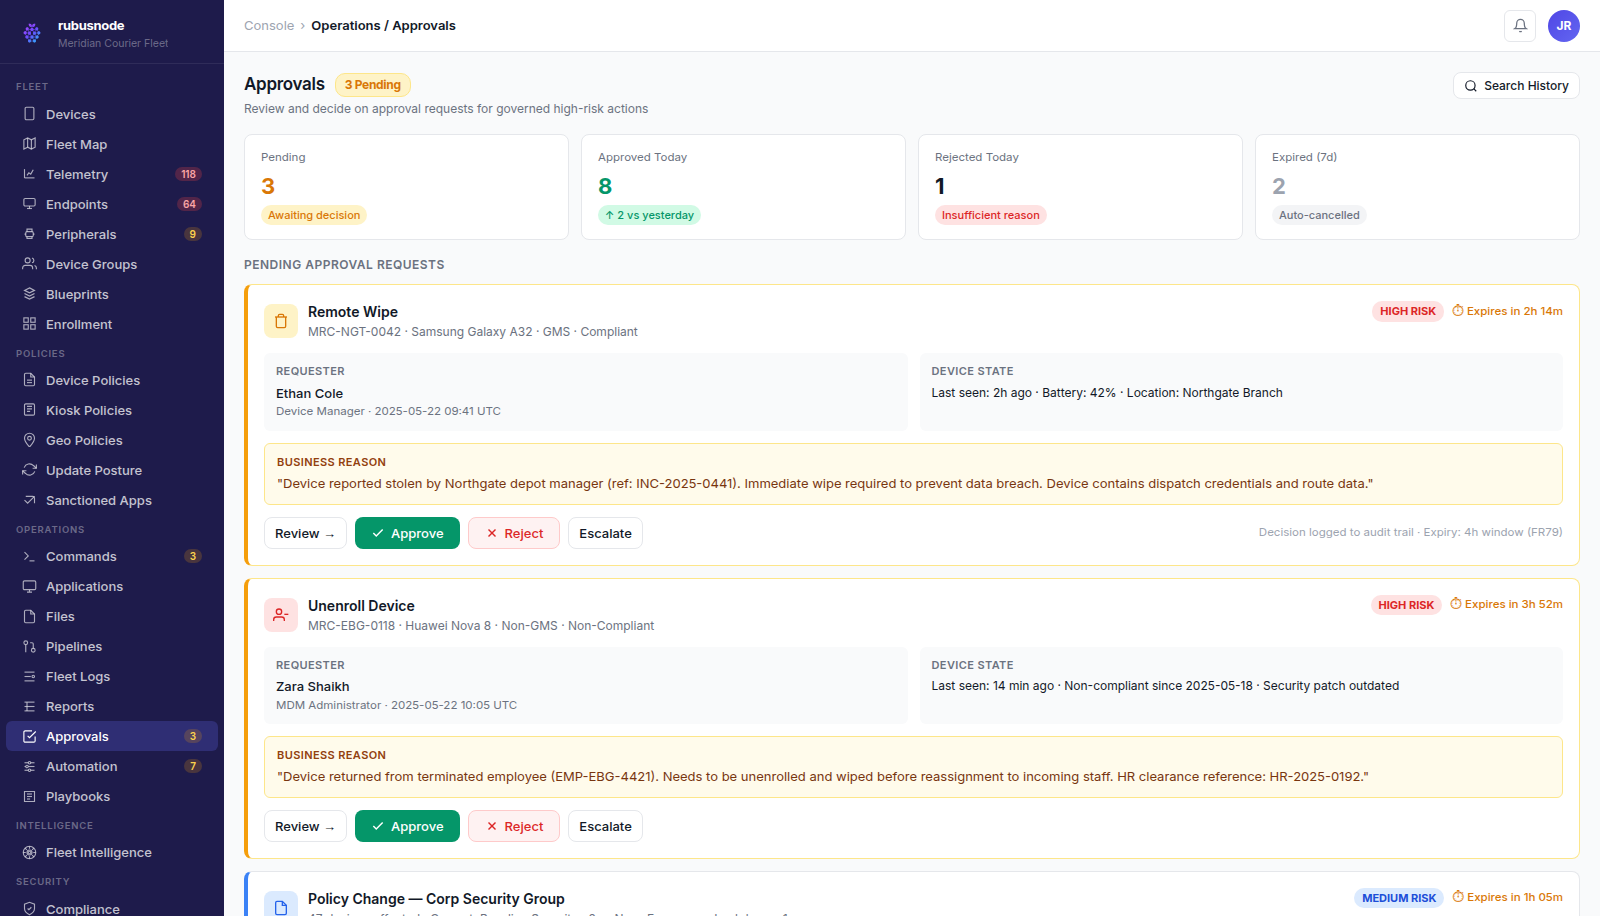
Approval-gated execution in the RubusNode console.
Dry-run before live execution
New automation rules start in dry-run observation mode, showing exactly which devices and events would have triggered the rule, before anyone flips it to live.
- Trigger-based rules on device, policy, and trust events
- Dry-run and impact preview before a rule goes live
- Approval-gated execution for high-risk remediation
Playbooks and event correlation
Safe playbook templates encode common remediation sequences. Event correlation and suppression prevent alert storms from a single underlying incident from triggering redundant automated actions.
Rollback and history on every run
Every automated action is recorded with rollback capability and full run history, so remediation stays accountable to the same audit standard as manual operator actions.
Common questions
Can automation rules take destructive actions like remote wipe?
High-risk actions run through the same approval-gate as manual operator actions — automation does not bypass approval for sensitive operations.
See how RubusNode fits your endpoint fleet.
Book a walkthrough for this capability and the rest of the platform.