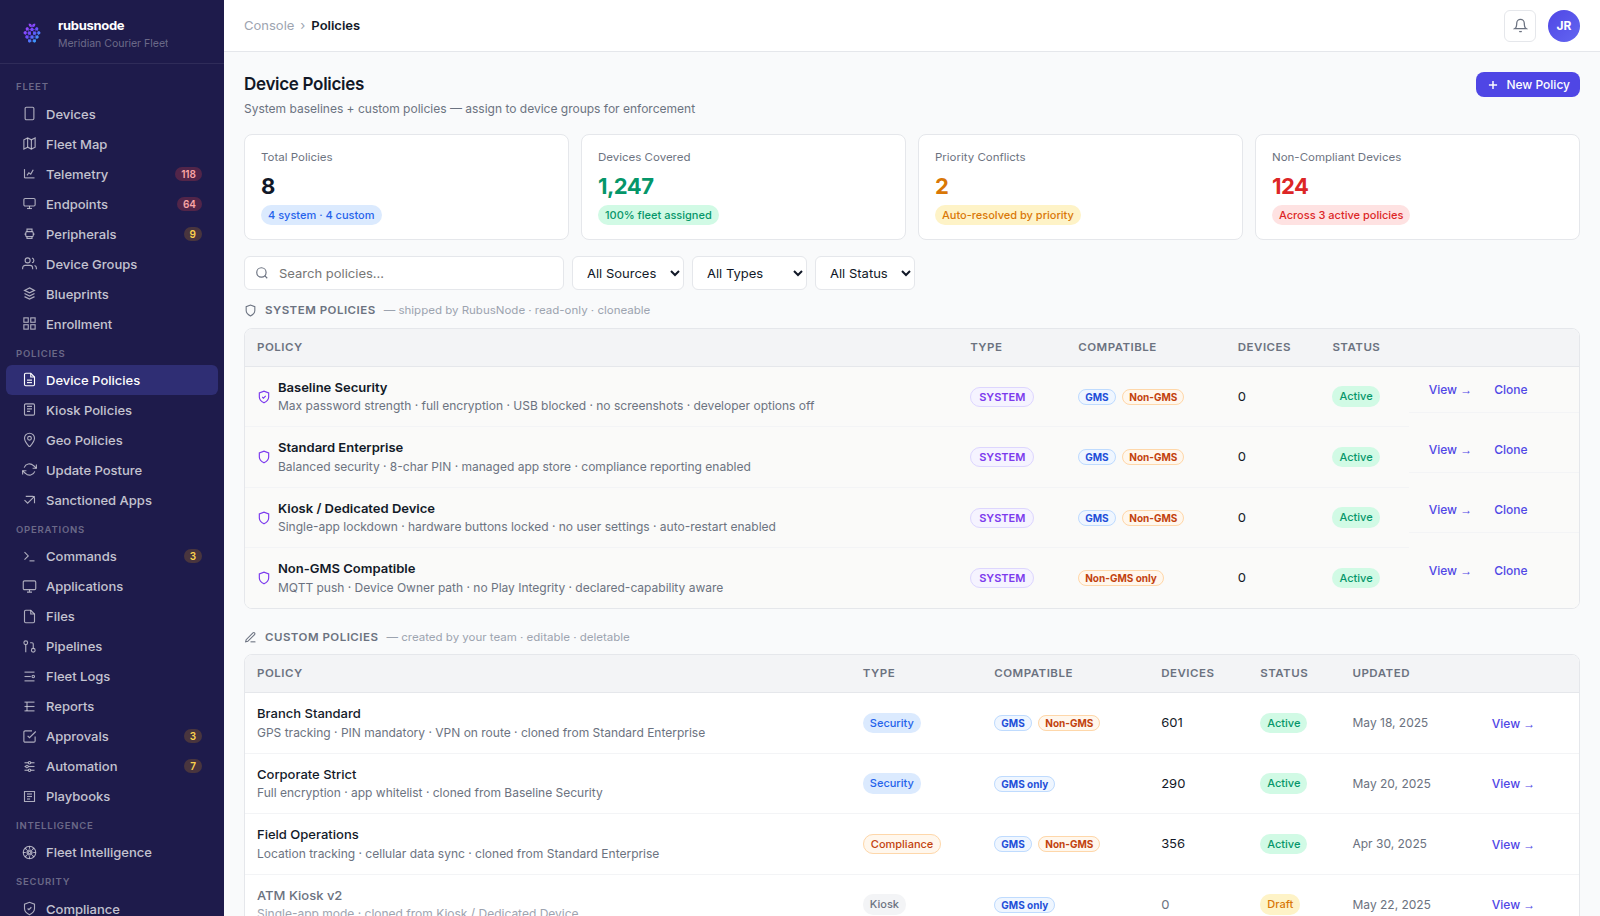
Policy baselines and rollout status in the RubusNode console.
Baselines with a safe rollout path
System and custom policy baselines cover password strength, encryption, app whitelisting, geo-fencing, and update posture. Rollout preview shows exactly which devices a change affects before it goes live, and canary groups validate a change against a subset of the fleet first.
- System baselines: Baseline Security, Standard Enterprise, Kiosk/Dedicated, Non-GMS Compatible
- Custom policies clonable from system baselines
- Dry-run and canary rollout before fleet-wide enforcement
OS-update posture and geo-fencing
Update posture policy governs how and when devices apply OS updates. Geo-fencing ties device compliance to physical location, useful for branch, depot, or facility-bound device classes.
Compliance evidence, not just a compliant/non-compliant flag
Every policy evaluation produces exportable evidence — which policy version, which devices, which result, and when — for regulated reviews rather than a point-in-time compliance percentage alone.
See how RubusNode fits your endpoint fleet.
Book a walkthrough for this capability and the rest of the platform.